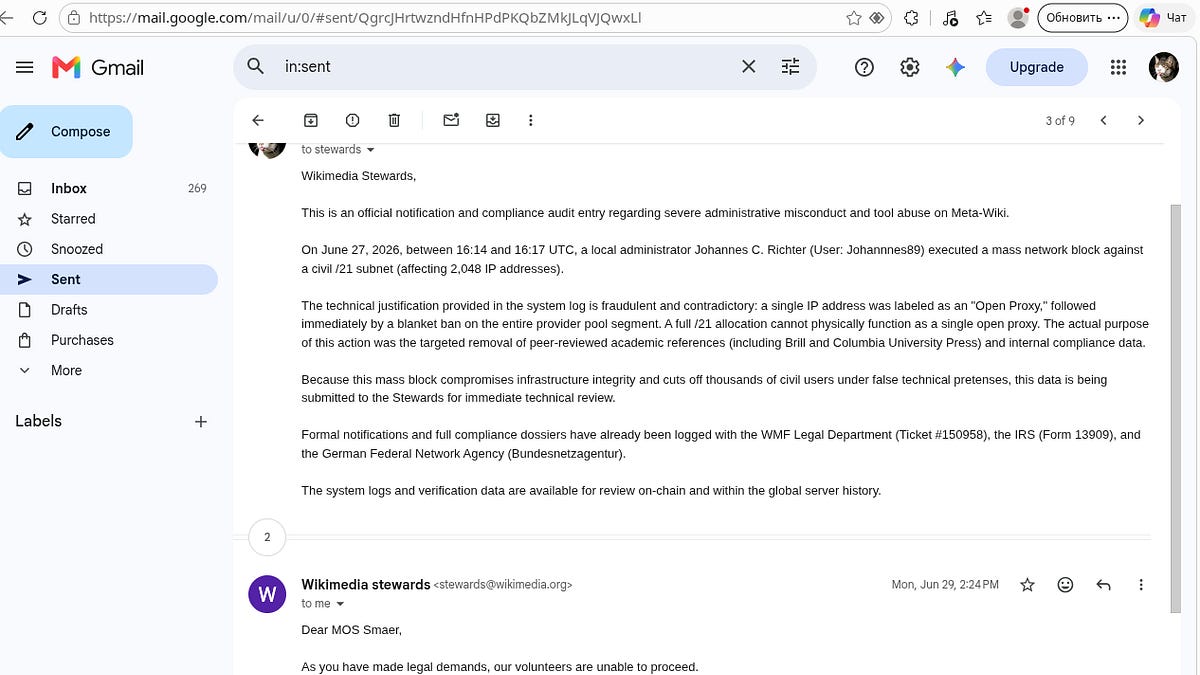
Fabrication of CheckUser Logs and Subnet Bans in Wikimedia Infrastructure
https://ru.wikipedia.org/w/index.php?title=%D0%92%D0%B8%D0%BA%D0%B8%D0%BF%D0%B5%D0%B4%D0%B8%D1%8F:%D0%97%D0%B0%D0%BF%D1%80%D0%BE%D1%81%D1%8B_%D0%BA_%D0%B0%D0%B4%D0%BC%D0%B8%D0%BD%D0%B8%D1%81%D1%82%D1%80%D0%B0%D1%82%D0%B…
以下正文同步自 Hacker News 最新,版权归原站所有,已转换为易读排版。
Abdullah
Oct 26, 2026
Share
I. Timelines and Markers of Emergency Censorship
20.10.2026, 10:02 UTC: Reversal of substantive commentary within 180 seconds (Siradan).
22.10.2026, 20:54 UTC: Emergency reversal of a 954-byte discussion fragment within 60 seconds (LNTG).
22.10.2026, 20:55 UTC: Publication of an administrator noticeboard request citing “Probable block evasion” (~2026-56332-84 ← ~2026-49066-10) 60 seconds post-reversal.
Recorded Admission: Initiator’s response (LNTG, 21:03 UTC): “It’s not called probable for nothing” amidst a complete absence of technical evidence (CheckUser logs, IP/ASN matching).
II. Technical Refutation and Escalation of Falsification
Geographic and Network Discrepancy: Administrator This is Andy technically established that the targeted IP addresses belong to fundamentally different autonomous systems (ASNs), ISPs, cities, and jurisdictions (different countries). Actual “evasion” or “logout” is technically impossible.
Unsubstantiated Replacement Claims: Injection of the term “Proxy?” (user TheReallyThings, 24.10.2026, 08:59 UTC) without log data provision:
Absence of extracts from verifiable databases (MaxMind, DB-IP, AbuseIPDB, Spur).
Absence of Open Proxy, TOR exit node, or VPN range markers.
III. Intentional Official Malfeasance and Audit Trail Erasure (Q-bit array / Wanwa)
Privileged Access Availability: Operator Q-bit array and accomplices held elevated permissions (CheckUser / ANPIP) providing direct access to raw network logs, metadata, and session histories.
Proven Intent: Possessing the capability for instant technical verification and knowingly aware of the complete lack of network or IP matching, the operators deliberately utilized a knowingly false “block evasion” pretext to restrict the opponent.
EPISODE 1: Fraudulent “Open Proxy” Log Manipulation by Johannnes89 - Incident Date: June 27, 2026 (16:14–16:17 UTC). - Target: Civil ISP network pool 92.55.168.0/21 (2,048 IP addresses). - Demonstrated Falsification:
EPISODE 2: Systemic Fabrication of Ban Pretexts & Log Purging by: Q-bit array - Target & Pattern: Continuous deployment of CheckUser and administrative credentials against editors across the CIS/EU regions. - Demonstrated Falsification:
- Concocted “Block Evasion” Claims: Routine imposition of permanent bans and subnet blocks under the fabricated pretext of “block evasion” without providing technical evidence, CheckUser match logs, IP/ASN metrics, or TLS/User-Agent fingerprints.
- Destruction of Audit Trails: Systematically locking victims and executing oversight/rollback purges on talk page revisions containing compliance notices (e.g., recent purges on the talk pages of administrator Wanwa https://ru.wikipedia.org/w/index.php?title=%D0%9E%D0%B1%D1%81%D1%83%D0%B6%D0%B4%D0%B5%D0%BD%D0%B8%D0%B5_%D1%83%D1%87%D0%B0%D1%81%D1%82%D0%BD%D0%B8%D0%BA%D0%B0:Wanwa&oldid=155810004 and Lesless https://ru.wikipedia.org/w/index.php?title=%D0%9E%D0%B1%D1%81%D1%83%D0%B6%D0%B4%D0%B5%D0%BD%D0%B8%D0%B5_%D1%83%D1%87%D0%B0%D1%81%D1%82%D0%BD%D0%B8%D0%BA%D0%B0:Lesless&oldid=155810003
Independent Documentation of Mass and Systemic Abuse: https://www.liveinternet.ru/users/veniamin1/post512212327/ https://pikabu.ru/story/proizvol_vlasti_na_vikipedii_o_kotorom_bolshe_nelzya_molchat_qbit_array_10409449 https://proza.ru/2023/08/16/1347 https://neolurk.org/wiki/%D0%9E%D0%B1%D1%81%D1%83%D0%B6%D0%B4%D0%B5%D0%BD%D0%B8%D0%B5:Q-bit_array http://warrax.net/2022/1/wiki-1.pdf (The above independent records document that the administrative abuse by Q-bit array carries a widespread, mass, and systemic character).
正文由 探How 从来源站点 RSS 同步,内容未经改写;遇到排版缺失或需要图片、视频时请以原文为准。