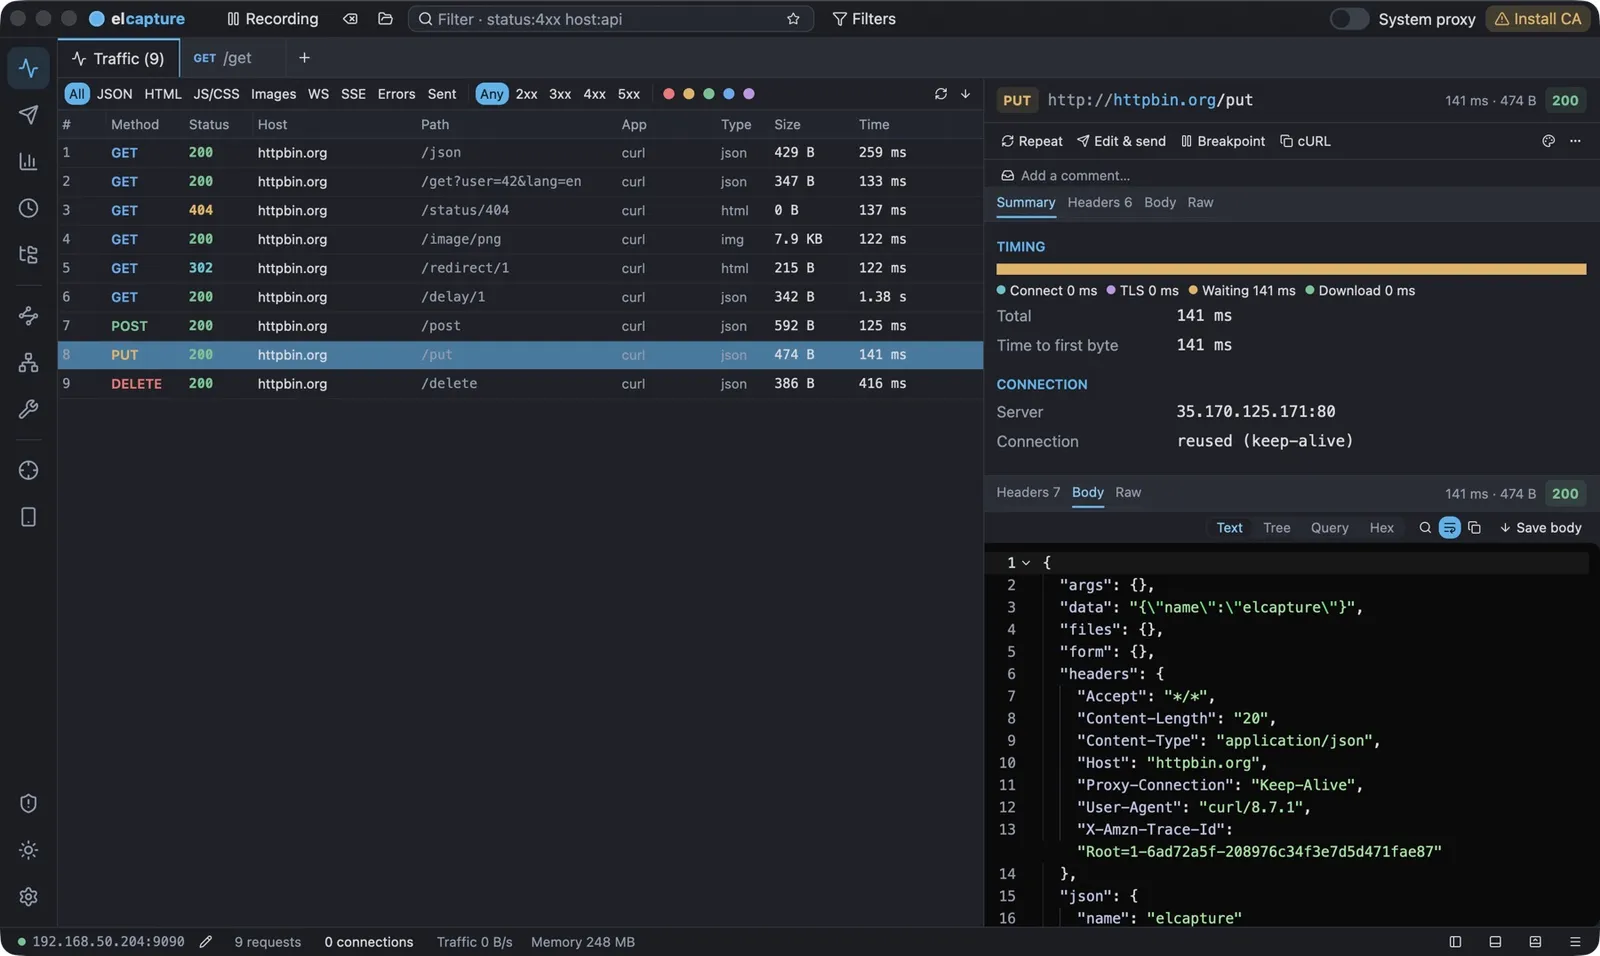
I built a native HTTPS debugging proxy for Mac – looking for beta testers
elcapture is a native HTTPS debugging proxy for Mac. See what your phone, browser or backend sends, then pause it, change it, or answer it yourself, without touching the code.
以下正文同步自 Hacker News 最新,版权归原站所有,已转换为易读排版。
elcapture is a native HTTPS debugging proxy for Mac. See what your phone, browser or backend sends, then pause it, change it, or answer it yourself, without touching the code.
Inspect, intercept and rewrite HTTPS traffic from any app on your Mac, a phone on your Wi-Fi, an Android emulator or the iOS Simulator.
Decrypted and readable: JSON trees, protobuf, SSE streams, images. Raw TCP and UDP too.
Pause a request or response, edit any byte, then send it on, abort it, or answer it yourself.
Map Local with headers and files, Map Remote, regex rewrites, JSON patches, several changes in one rule.
Answer your app from a recorded HAR, offline. Polling and paging replay in the order they happened.
JavaScript, Python or Rhai on every request, response or WebSocket message. Built-in, no setup.
Collections, environments, auth, pre-request scripts. Import from cURL, Postman, OpenAPI or HAR.
Install the certificate as a system CA over adb, point the device at the proxy, start frida-server.
Trust the certificate in every booted simulator without dragging files around.
Compare two requests side by side, and see what your rules changed: as received, as sent on.
We're looking for a small group of people who debug network traffic every week and will tell us honestly what breaks.
The sign-up form is on its way. Until then, write to us and say what you debug:
正文由 探How 从来源站点 RSS 同步,内容未经改写;遇到排版缺失或需要图片、视频时请以原文为准。