Plex vulnerabilities being exploited in the wild to drop a cryptominer
Back on September 1st, 2026, Plex sent out emails and did a security announcement regarding important security updates. See the post here: https://forums.plex.tv/t/important-security-update-for-plex-media-server-v1-43-2…
以下正文同步自 Hacker News,版权归原站所有,已转换为易读排版。
Back on September 1st, 2026, Plex sent out emails and did a security announcement regarding important security updates. See the post here: https://forums.plex.tv/t/important-security-update-for-plex-media-server-v1-43-2-and-earlier/942319
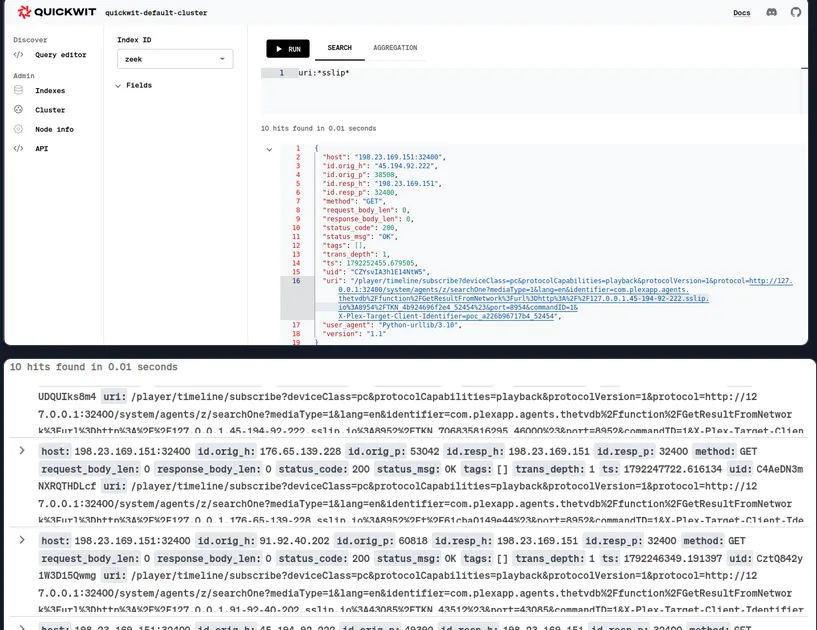
As an infosec person and a Plex user, I was really curious about what this vuln was and if I could see in-the-wild exploitation. I set up a honeypot w/ a vulnerable Plex version running.
The details were limited and they said that they'd update the page with more details so I kept watching and didn't see anything.
Finally, on Sep 26th, I saw some CVE's get published here: https://www.cvedetails.com/vulnerability-list/vendor_id-14994/year-2026/Plex.html but none of them had CVSS score of 9+. They did contain a link to a blog post which was not released at the time.
Link was to https://zmain.info/blog/plex2shell and release was supposed to be mid Oct so I waited and finally saw an update on Oct 16th (yesterday). The author had discovered and chained several vulns together to get remote code exec which was pretty cool.
正文由 探How 从来源站点 RSS 同步,内容未经改写;遇到排版缺失或需要图片、视频时请以原文为准。