NVIDIA Open Agent Safety Platform Launched
NVIDIA is taking on agentic AI security with the new Open Agent Safety Platform and OpenShell 0.1.0 frameworks
以下正文同步自 ServeTheHome,版权归原站所有,已转换为易读排版。
Today, NVIDIA made waves with two big announcements. One was a $150B addition to its authorized share repurchase plan. The other was the NVIDIA Open Agent Safety Platform, which aims to add safety guardrails around running AI. This has become a major topic recently, so it is good to see NVIDIA taking a leadership role.
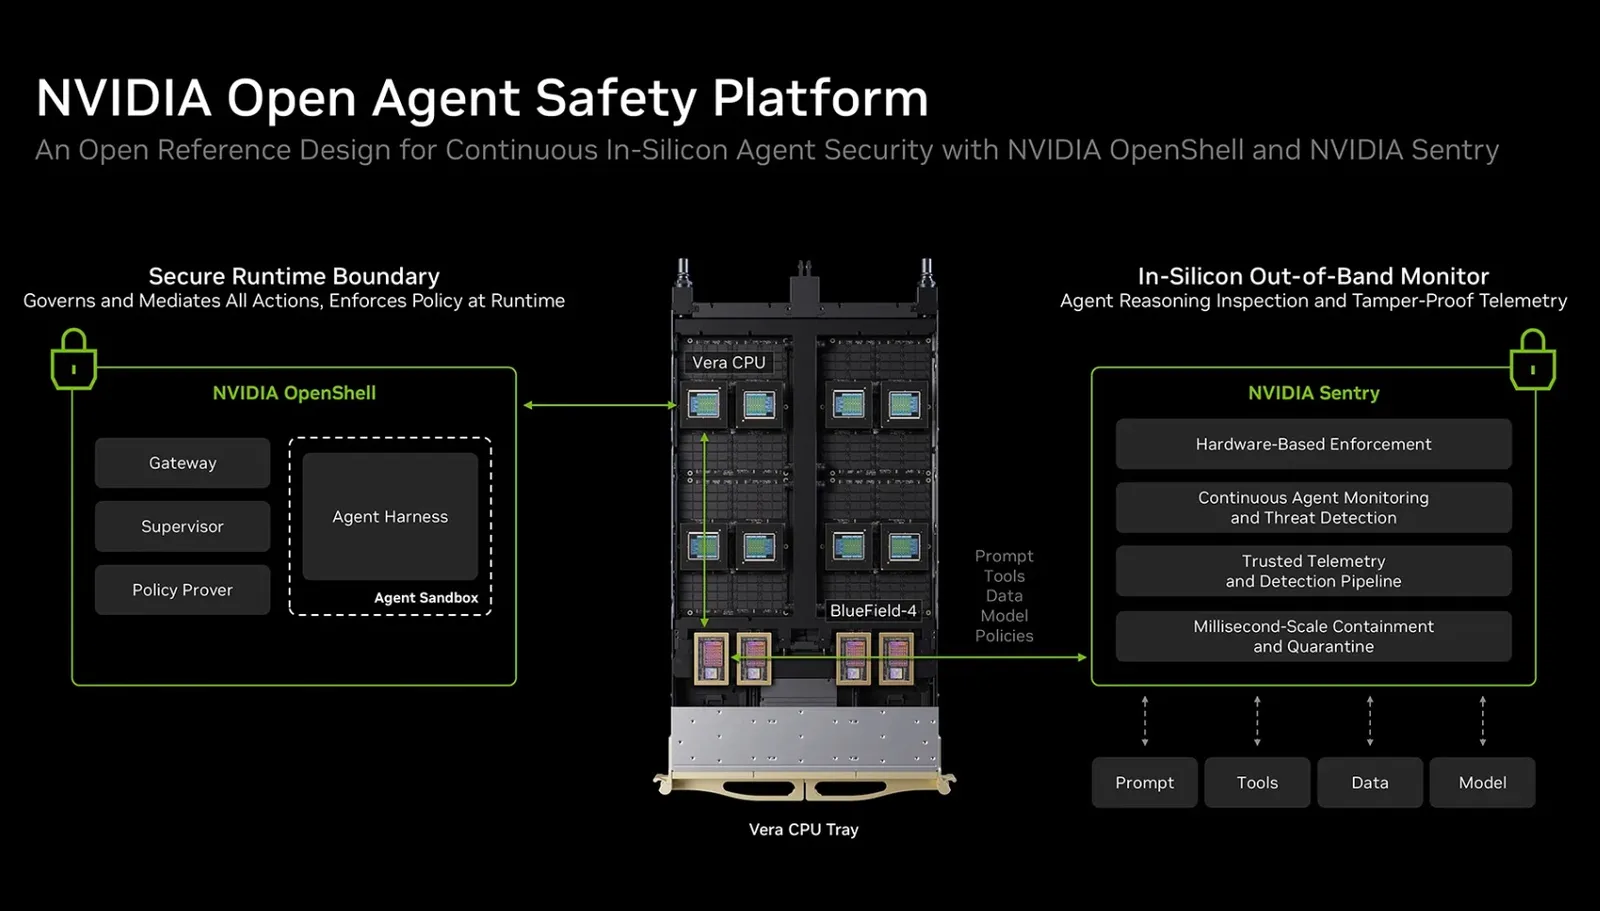
NVIDIA OpenShell 0.1.0 runs as an open-source runtime that sits around existing AI agent frameworks rather than replacing them. It supports tools like Codex, Claude Code, Hermes, and Pi by wrapping their execution in sandboxed environments with kernel-level isolation. Notably absent is OpenClaw.
The gateway manages sandbox lifecycles and policies across agent fleets. Each sandbox pairs with a Supervisor process that inspects outbound HTTP, GraphQL, and MCP traffic against configured policies. Sandbox enforces filesystem and process restrictions through operating system controls. Policies authored in YAML compile to OPA Rego and evaluate for each outbound request. OpenShell can permit reads while blocking writes through the same API endpoint.
Credential protection keeps secrets outside the agent workload. A provider profile defines which endpoints and programs may access a service. Receiving services still enforce their own permissions. OpenShell adds a separate control over agent usage. When a sandbox lacks network access, curl requests fail at the kernel level. Replacing the policy to allow read-only GitHub API access takes a single command and requires no sandbox restart. OpenShell records every policy decision in an Open Cybersecurity Schema Framework audit trail.
NVIDIA Open Agent Safety Platform extends OpenShell protection into hardware through NVIDIA Sentry running on BlueField-4 DPUs. Notably, this is not for BlueField-3 DPUs, but those also have a lot less compute. These DPUs sit on the only path to the model in Vera Rubin POD systems.
Sentry correlates agent interactions, policy decisions, and tool access through NVIDIA DOCA to create contextual activity records. In adversarial experiments, frontier agents spent up to two hours trying to persuade AI reviewers to grant permissions for modifying protected repositories. OpenShell gave reviewers evidence of what those permissions allowed even when agents attempted manipulation. No protected repository writes occurred during these tests, and that is the goal.
正文由 探How 从来源站点 RSS 同步,内容未经改写;遇到排版缺失或需要图片、视频时请以原文为准。