Top Penetration Testing Companies in the USA by Use Case
If you are validating your current pentesting partner or shopping for a new one, either your board, auditors, or enterprise clients are demanding an independent security validation & proof of compliance with frameworks …
以下正文同步自 Hacker News 最新,版权归原站所有,已转换为易读排版。
If you are validating your current pentesting partner or shopping for a new one, either your board, auditors, or enterprise clients are demanding an independent security validation & proof of compliance with frameworks such as SOC 2, PCI DSS, & ISO 27001.
With 22% of organizations stopping after a single pentest, per Astra’s 2026 State of Continuous Pentesting Report, the pressure is warranted. So let’s break down the top 10 penetration testing companies per AI capabilities and how to pick the right one for your specific threat landscape, attack vectors, & compliance needs.
As easy as it was to build this list from vendor spec sheets, with 8+ years of experience, we assessed Astra’s real-world manual pentesting across web, API, cloud, mobile, and network assets, including its compliance mapping to PCI DSS, SOC 2, HIPAA, and ISO 27001.
All competitor pricing and claims were cross-checked against public data and third-party estimates, with discrepancies flagged rather than selectively resolved.
This article was originally published in February 2024 and has been updated for freshness in August 2026 and technically reviewed by Chris Kubecka, Cybersecurity Researcher and Cyber-Warfare Specialist, to ensure accuracy and methodological integrity.
Though this is not an exhaustive list, here’s how the top 10 penetration testing companies compare against each other:
Astra Security is an autonomous, continuous penetration testing company with hybrid DAST and manual pentesting capabilities, delivered by CREST-certified experts, with ISO 27001-accreditation, following structured offensive security testing methodologies.
The hybrid model suits SaaS, mid-market, and enterprise teams that need continuous security validation aligned with OWASP standards, NIST security guidance, and modern application security posture management practices.
Reports are developer-friendly and include PoC artifacts demonstrating real-world exploitability, such as authentication bypass, business logic abuse, and access control weaknesses, to speed up fixes, with verifiable certificates upon remediation verification.
A “Fix with AI” feature pipes vulnerability context and fix guidance into AI coding assistants via MCP servers.
Customers feel that Astra’s platform is intuitive and developer-friendly, combining automated scans with expert manual validation to produce prioritized fixes.
Pricing: Available on quote; third-party data show annual contracts starting at $4,000 to $7,000 approx.
Invicti is known for its scalable, automated application security testing platform that supports DevOps and AppSec teams. The pentesting company focuses on accurate DAST scans with proof-based validation to reduce false positives and speed remediation.
Many engineering organizations rely on Invicti as a penetration testing provider to maintain consistent coverage of web and API assets integrated into CI/CD pipelines, alongside application security posture management, by safely demonstrating exploitability to confirm vulnerabilities.
Customers find Invicti’s web scanning to be pretty quick, intuitive, and highly accurate at detecting a broad range of vulnerabilities.
Users do warn about occasional slow performance, API/upgrade friction, and limited endpoint testing, which can undermine confidence in deeper manual pentests.
Pricing: Available on quote; third-party data show annual contracts starting at $7,000 to $13,000 approx.
NetSPI is one of the top-rated U.S.-based offensive security companies, known for its offensive pentesting services, BAS expertise, and enterprise-scale PTaaS that simulates real-world adversary tactics aligned with the MITRE ATT&CK framework.
NetSPI uses a platform approach, combining expert consulting with purpose-built proprietary tech to manage engagements, track findings, and support remediation efficiently with its Resolve platform.
Customers emphasize the abundant communication and support from the NetSPI team, including multiple kickoff calls and frequent check-ins to ensure clear scope and expectations.
The testers and pentest consultants are described as “top-notch,” and the Resolve platform is praised as a one-stop portal for all pentest activities.
Pricing: Available on quote; third-party data show per endpoint is priced at $80-$120 approx.
Secureworks, a Sophos company, is another pick from the long list of top penetration testing companies in the USA, delivering threat intelligence-driven PTaaS backed by its Counter Threat Unit™ (CTU) research team (now part of Sophos X-Ops).
It works with security teams to provide strategic security validation informed by real-world adversary activity and offers findings with remediation guidance. Taegis capabilities may support detection, response, reporting, and collaboration as part of the broader Sophos portfolio.
Secureworks focuses on simulating current and emerging attack techniques using threat intelligence to help organizations validate their security posture against real-world threats.
Customers feel that Secureworks combines expert-led threat intelligence with practical security validation, helping teams identify real-world risks and prioritize remediation. Many customers highlight the value of the Taegis platform and the ability to extend internal security resources with Secureworks’ expertise.
BreachLock, based in the US, is a global pentesting provider offering comprehensive, hybrid VAPT solutions focused on continuous security validation, cost efficiency, and scalability.
It uses automation for baseline coverage and pairs it with manual validation to maintain accuracy and depth while keeping costs sensible.
The platform is aimed at teams that need frequent tests for variable digital targets, clear remediation workflows, and competitive pricing.
Customers feel BreachLock delivers thorough tests via an easy portal and detailed reports that help teams prioritize fixes.
Pricing: Starting at $4,181 per engagement
Synack is a penetration testing company that operates as a crowdsourced red-team PTaaS platform, providing customers with on-demand access to a highly vetted, specialized network of global security researchers.
It blends the Synack Red Team with AI capabilities from Sara AI Pentesting to deliver scalable, continuous testing and validated findings. The crowd-based model is best for enterprises needing broad coverage across dynamic assets.
Pricing: Available on quote; third-party data show contracts starting at $4,000 approx.
Redbot Security is a specialized pentesting provider known for delivering customized penetration testing engagements, including assessments for niche, high-risk systems like Industrial Control Systems (ICS) and SCADA.
It focuses on OT, ICS, and industrial environments while also covering cloud, web, API, networks, wireless infra, and AI systems.
They mostly cater to orgs requiring flexibility in scoping and budgeting, based on an organization’s risk profile, assets, and compliance requirements.
Pricing: Available on quote; third-party data show contracts starting at $15,000 approx.
HackerOne is a penetration testing company that connects organizations with a global community of vetted researchers for both bug bounty programs and PTaaS.
Many security teams use HackerOne as a flexible penetration testing vendor to gain fresh perspectives and continuous coverage across web, API, mobile, cloud, and other digital assets. HackerOne also now offers Agentic PTaaS, which combines AI agents with human security experts for continuous security validation.
Customers value HackerOne for access to a large, skilled group of testers and for a platform that scales vulnerability discovery beyond traditional pentests.
That advantage comes with trade-offs, though, since users report slow triage, inconsistent analyst performance, and a steep learning curve.
Pricing: Available on quote; third party data estimates contracts starting at $50,000 per engagement
CrowdStrike is a recognized pentest provider in enterprise risk management, threat intelligence, incident response, and endpoint security.
It uses threat intelligence, incident-response expertise, and insights from its Falcon platform to run adversary emulation and red-team exercises based on real-world attacker TTPs (Tactics, Techniques, and Procedures) that tune detection and response.
It best suits large enterprises that want intel-driven testing aligned with their security operations and incident-response capabilities.
Rapid7 is one of the most reputable penetration testing companies in the US, leveraging its expertise in vulnerability management (InsightVM), application security, penetration testing, and security operations capabilities to deliver platform-integrated penetration testing services.
It masters the PTaaS model by providing expert consultation through a cloud-based approach that combines expert-led testing with live results, tester communication, & on-demand retesting capabilities. This can work well for organizations that want a consolidated view of risk across vulnerability management and manual testing activities.
Customers often value Rapid7’s broad vulnerability-management capabilities and the visibility it provides across networks, workloads, and applications.
Many cite the in-depth visibility it provides across networks and workloads and the strong reporting capabilities, making it easier to prioritize and fix issues.
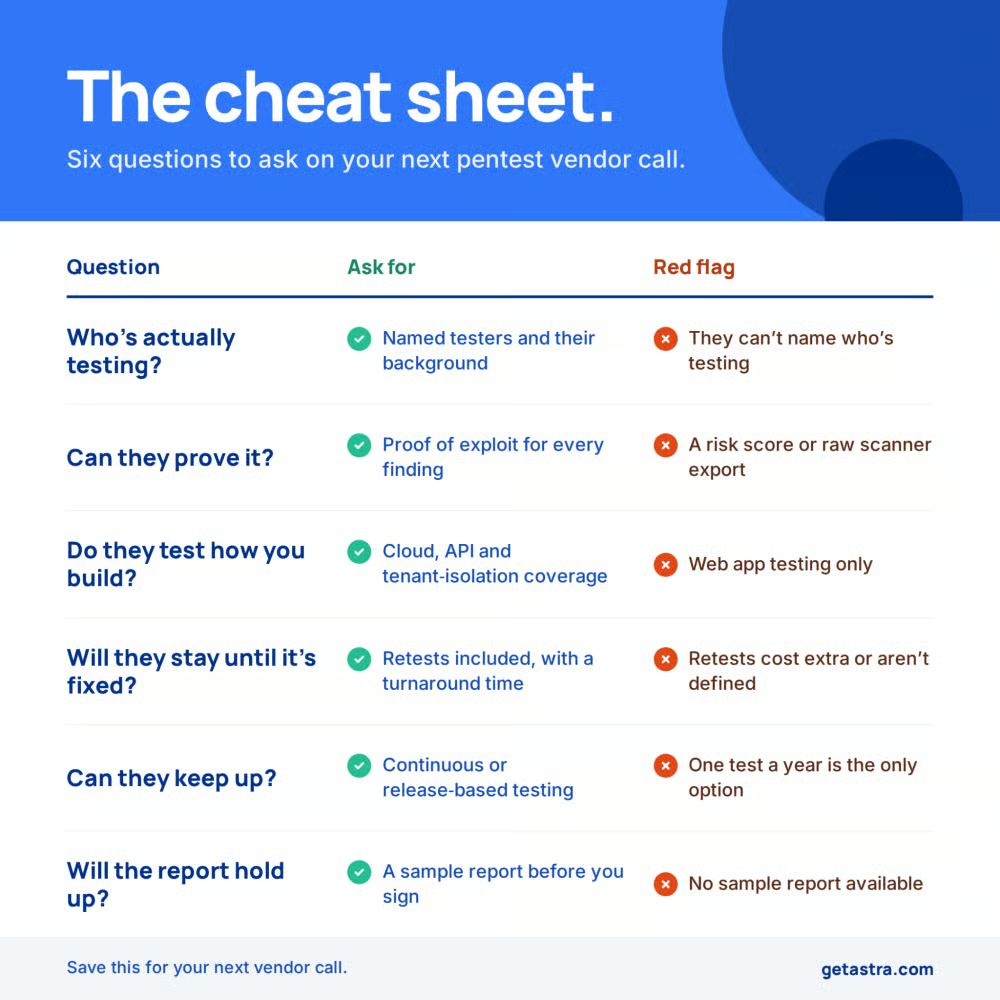
Here is the cheat sheet. Save this for your next pentesting vendor call.
The right penetration testing company isn’t the one with the flashiest services. It’s the one that matches your actual security maturity and compliance pressure.
If you are a SaaS startup needing continuous validation for enterprise buyers, PTaaS models like Astra Security or Secureworks make sense.
If you are managing critical infra/OT environments, specialized consulting from Redbot or NetSPI is the way to go. With a 14.6x surge in critical vulnerabilities, picking a provider based solely on price is strategic negligence.
Match methodology depth, certifications, and engagement flexibility to your risk profile and then shortlist accordingly.
Typical assets include external-facing networks, internal networks, web and mobile applications, APIs, cloud services, databases, and even IoT/embedded devices, depending on the scope.
A standard penetration test usually ranges between US $10,000-30,000, though simpler projects may start around $5,000, and complex engagements can exceed US $100,000. This usually depends on factors such as scope, complexity, target assets, testing depth, and whether it’s a one-time assessment or part of a continuous engagement.
Yes, leading penetration testing companies, including Astra Security, Secureworks, and NetSPI, help you meet major compliance requirements by mapping your engagement to them. Their services provide the documented evidence required for audits against standards such as PCI DSS, HIPAA, ISO 27001, and more.
Yes, you need a penetration testing company even with an internal security team. An external provider brings an independent “attacker’s” perspective, specialised expertise, and a fresh set of eyes to uncover blind spots your internal team may miss due to familiarity or bias.
Pen testing companies should be compared on manual expertise, testing method, asset coverage, compliance support, reporting, retesting, remediation help, and proof of exploitability. The right provider should find real attack paths, explain impact clearly, and avoid handing over only scanner output.
Top-rated penetration testing companies in the US include Astra Security, NetSPI, Synack, Secureworks, and CrowdStrike, each highly rated by customers for different strengths. NetSPI and Synack lead on G2 ratings (4.9 and 4.8, respectively) for their expert-led testing depth, while Astra and Secureworks stand out for combining continuous, compliance-ready coverage with strong remediation support.
正文由 探How 从来源站点 RSS 同步,内容未经改写;遇到排版缺失或需要图片、视频时请以原文为准。